Managed Kubernetes, reimagined · In development

Control that scales.
Privacy that stays.

Managed Kubernetes, reimagined. We are building a platform that runs the control plane, provisions your nodes, and handles all the networking between them. You just provide the servers. Your workloads, your hardware, your data.

Add any server with one command

curl -sL orista.eu/join | sh

Managed control plane. Your worker nodes. One unified cluster.

Your Metal. Our Mind.

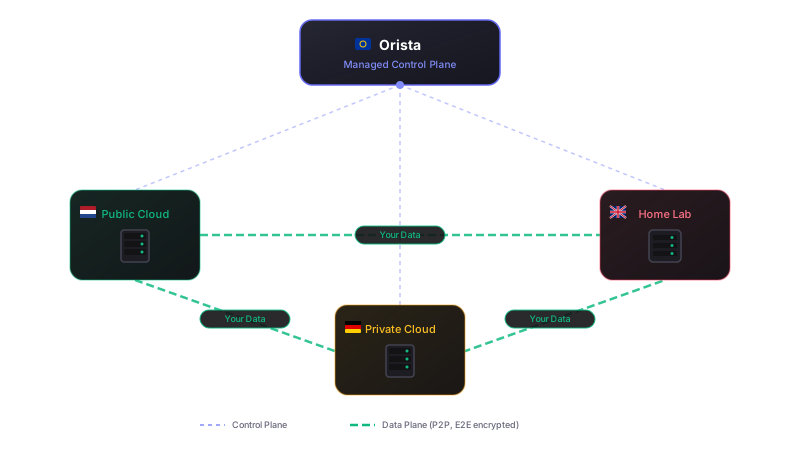
Traditional managed Kubernetes locks you into their infrastructure. We believe in a different model: Bring Your Own Nodes. Orista runs the Kubernetes control plane; you connect worker nodes from anywhere: your public cloud account, your private data center, or the server under your desk.

Orista manages
Control Plane + Node Operations
Kubernetes control plane (API, scheduler, etcd)
Node networking & mesh connectivity
Updates, patches & monitoring (planned)
You provide
The Hardware
Any Linux server becomes a node
Your cloud, data center, or home lab
Data stays on your machines

The Orista Edge

What we are building, and why.

Stupidly Simple

One Command to Join

Turn any Linux machine into a Kubernetes worker node. No agents to configure. No network setup. No kubeadm. Run one command and it joins your cluster instantly, even behind NAT, even without a public IP.
$ ssh your-server
curl -sL orista.eu/join | sh
✓ Connected to mesh
P2P mesh network showing secure direct connections between nodes across different networks

European Compliance

US providers face CLOUD Act subpoenas. We don't. European entity, EU jurisdiction, control plane hosted in the EU.

Designed with NIS2, DORA and BIO in mind
GDPR · Schrems II
No US jurisdiction

Bring Any Server

Mix and match. Public cloud, private data center, bare metal, or a Raspberry Pi. If it runs Linux, it can securely join your cluster.

AWS, GCP, Azure
Hetzner, OVH, Scaleway
On-prem & Home Lab

Your Data Stays Home

Workloads run on your servers. Traffic flows between your nodes. We orchestrate and we never see your data.

Zero data plane access
Direct node-to-node traffic
Your keys, your storage
60s
To join a node
0
Open ports needed
P2P
Direct node traffic
E2E
Encrypted always

From Zero to Cluster in 60 Seconds

No DevOps degree required. Seriously.

1

Deploy the Mind

We spin up a dedicated Kubernetes control plane for you, in our European region.

2

Connect Your Servers

Run one command on any Linux machine. Behind NAT? No public IP? Strict firewall? Doesn't matter, it connects and joins the mesh automatically.

3

Deploy Anywhere

Your nodes talk directly to each other; encrypted, peer-to-peer. Deploy workloads across clouds as if everything was on a single private network.

Terminal
# Join any server - even behind NAT with no public IP
$ curl -sL https://orista.eu/join | sh -s -- --cluster my-cluster
Detecting hardware... 8 vCPU, 32GB RAM, 500GB NVMe
Network: Behind NAT, no public IP detected
Establishing P2P mesh tunnel... Connected
Verifying E2E encryption... Active
Joining cluster... Ready
Node office-server-01 joined the mesh.
Peers discovered: aws-eu-west-1, hetzner-fsn1, home-lab-pi

Where we are

Orista is under development. Joining nodes across providers works in our prototype. Making a cluster behave well over the public internet is what we are working on now.

Working in prototype
  • Dedicated control plane per cluster in a European data center
  • One-command join for any Linux server
  • Encrypted WireGuard mesh between nodes, also behind NAT
  • eBPF pod networking over the mesh (VXLAN overlay for now)
  • Node inventory and heartbeat
In development · 2027
  • Native pod routing over the mesh, without double encapsulation
  • Latency measurement between nodes and latency-aware scheduling
  • Failure detection that tells a dead node from a broken link
  • Verified node location, so workloads provably stay in a jurisdiction
Research · later
  • Storage that follows workloads across providers
  • Cost-aware scheduling across providers
  • Load balancing and ingress across providers, with SSL passthrough
  • Highly available control plane, automatic node updates
European Entity

Legally European.
Technically Private.

Orista is not a "Sovereign-washed" US service. We are a European entity, operating under European law. We run only the control plane; your data never touches our infrastructure. Your workloads, your traffic, your secrets: all stay on your servers, wherever they are.

EU Jurisdiction
EU Data Residency
Zero-Knowledge Architecture

Ready to reclaim your infrastructure?

Orista is under development. Read how it is designed and what we are working on.

Read the Whitepaper